 Anonymous


 emlen
в плеере могу каждую отдельно слушать
 Артем
ее поддержку же выпинули
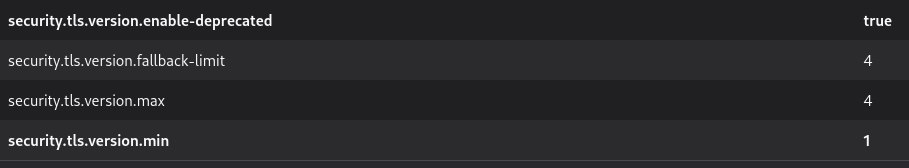
выкинули, на бубунте у коллег работает с такими настройками в 83 firefox ))
Anonymous
выкинули, на бубунте у коллег работает с такими настройками в 83 firefox ))
может в федоре что-то подкоректировали. Но в где-то 80 версии мне писало, что тлс 1 скоро все
Anonymous
всем привет
 Alexander
Цель запустить Винду с пробросом видюхи на Nvidia
Тогда лучше gentoo. Если хочешь развлечений, то развлекайся по полной.
По своему опыту скажу, что настраивать проброс видюхи ты будешь больше времени, чем играть :)
 Lev
Я тоже думал что генту
Lev
Но чёт компилировать гипервизор...
Lev
Хотя чёрт его знает, камушек i5-9400F
Anonymous
как узнать, какой юнит самый последний загрузился в системд?
emlen
вроде в cinerella что-то с горем пополам получается сделать с этими дорожками
emlen
еще бы понять как в ней не рендерить, но копировать видео
Anonymous
еще бы понять как в ней не рендерить, но копировать видео
Чтобы смикшировать аудиодорожки можно использовать инструменты попроще. Я бы их сначала извлёк, смикшировал в аудиоредакторе и результирующую дорожку добавил в видео.
avidemux и audacity
emlen
Чтобы смикшировать аудиодорожки можно использовать инструменты попроще. Я бы их сначала извлёк, смикшировал в аудиоредакторе и результирующую дорожку добавил в видео.
avidemux и audacity
как вариант, спасибо, а может чем-нить типа ffmpeg это решаемо?
Anonymous
как вариант, спасибо, а может чем-нить типа ffmpeg это решаемо?
решаемо. Только с ним договариваться долго. А тут какой-никакой, но редактор с GUI
emlen
ну да сложновато (для меня), может рожу сценарий разово, чтоб потом юзать не задумываясь особо)
emlen
а есть вариант представить участок экрана в качестве устройства-веб камеры?
Anonymous
какой щас последний tgdesktop?
Anonymous
2.4.7
Anonymous
https : // i . imgur . com / soWMOQU . jpg
Anonymous
можите переслать в виде картинки
 Никита
https://i.imgur.com/soWMOQU.jpg
Anonymous
помогите пожалуйста. в remmina по RDP не работает звук на удаленном сервере
Anonymous
помогите пожалуйста. в remmina по RDP не работает звук на удаленном сервере
у меня pipewire стоит, везде кроме remmina есть звук
Anonymous
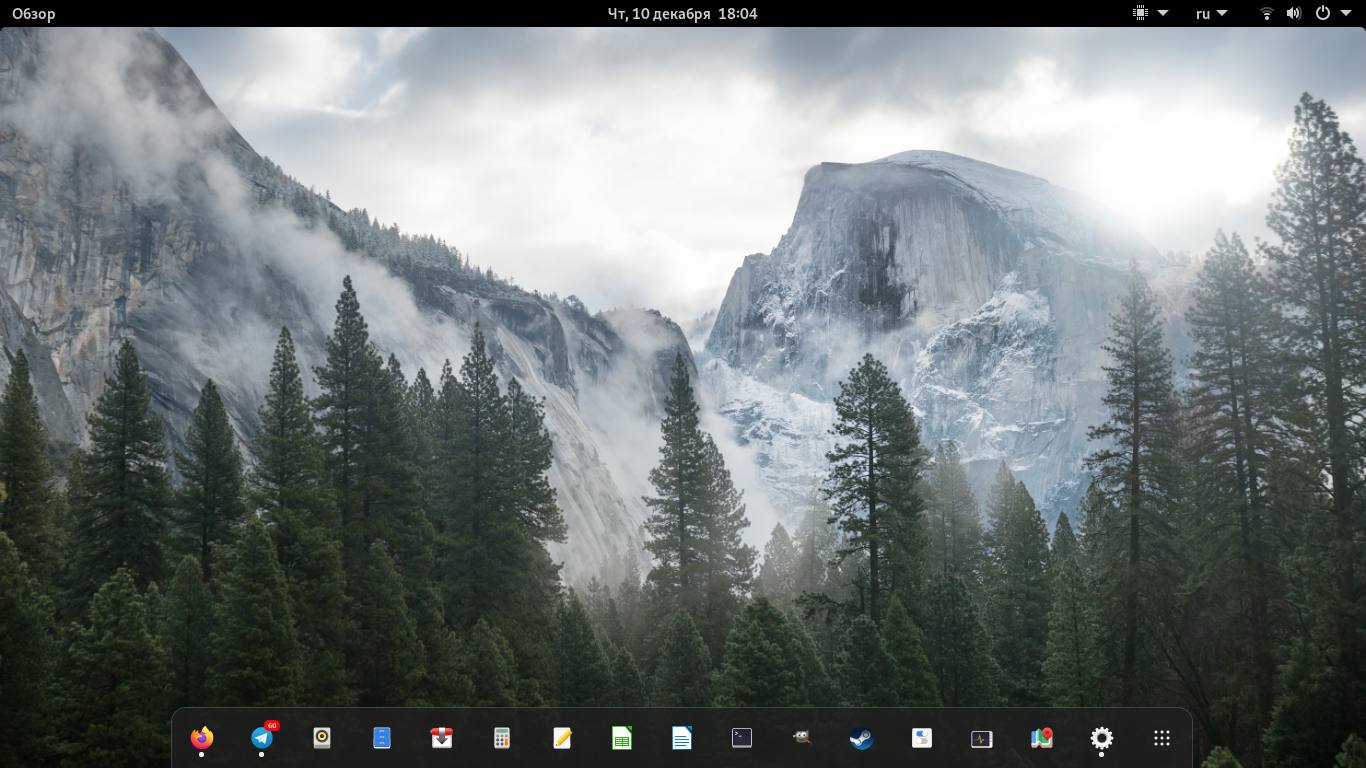
в обоях
Никита
зачем косить под нее?))
Anonymous
помогите пожалуйста. в remmina по RDP не работает звук на удаленном сервере
нах тебе rdp под линуксом?
Anonymous
vnc сервак подними
Anonymous
если надо принтер пробросить то cups
Anonymous
открытые реализации пропиетарного по обычно дерьмо
Anonymous
ты дебил
Никита
@Vascom2 , вмешайся плиз
Никита
я за бан
 linxon
а есть вариант представить участок экрана в качестве устройства-веб камеры?
если только попробовать v4l2loopback
Anonymous
By default, RFB is not a secure protocol. While passwords are not sent in plain-text (as in telnet), cracking could prove successful if both the encryption key and encoded password were sniffed from a network. For this reason it is recommended that a password of at least 8 characters be used. On the other hand, there is also an 8-character limit on some versions of VNC; if a password is sent exceeding 8 characters, the excess characters are removed and the truncated string is compared to the password.
UltraVNC supports the use of an open-source encryption plugin which encrypts the entire VNC session including password authentication and data transfer. It also allows authentication to be performed based on NTLM and Active Directory user accounts. However, use of such encryption plugins makes it incompatible with other VNC programs. RealVNC offers high-strength AES encryption as part of its commercial package, along with integration with Active Directory. Workspot released AES encryption patches for VNC. According to TightVNC,[15] TightVNC is not secure as picture data is transmitted without encryption. To circumvent this, it should be tunneled through an SSH connection (see below).
VNC may be tunneled over an SSH or VPN connection which would add an extra security layer with stronger encryption. SSH clients are available for most platforms; SSH tunnels can be created from UNIX clients, Microsoft Windows clients, Macintosh clients (including Mac OS X and System 7 and up) – and many others. There are also freeware applications that create instant VPN tunnels between computers.
An additional security concern for the use of VNC is to check whether the version used requires authorization from the remote computer owner before someone takes control of their device. This will avoid the situation where the owner of the computer accessed realizes there is someone in control of their device without previous notice.
 Anonymous
и где тут закос
 Vasiliy Glazov
Anonymous
я говорил использовать rfb?
Anonymous
зачем косить под нее?))
Кое-где они преуспели в дизайне, но это единственное, в чём они преуспели ;)
Anonymous
макось шикарная система
Anonymous
она намного ближе к unix чем linux
Anonymous
с кучей бекдоров
Anonymous
rdp умеет в передачу звука? Я в шоке.
 Sergei
@Vascom2 Тебе не кажется, что объём клоунады в чате достиг критического уровня?
Anonymous
А есть у нас товарищи на 1200 райзене? Я вот не понимаю, 4 потока для ворка это слишком мало или я делаю что-то не так? У меня конечно подкручен звук, но даже без музыки система ловит статтеры. На 1700ом такого не испытывал