 Où va le monde


вот файл который будет устанавливать и с=там есть строки которые качают это скакойто жопы
 Sergey
Для icu тарбол с сборанными бинарями можно скачать отсюда
https://github.com/unicode-org/icu/releases/tag/release-52-2
Прямая ссылка:
https://github.com/unicode-org/icu/releases/download/release-52-2/icu4j-52_2.tgz
Хеш-сумма: 5e544289cbc4a7c0d2ece535bece19785d5feead9b3b64d0d9671a413ca75a28
Для второго сам ищи))
Sergey
Ладно, вот тебе для libpng прямая ссылка:
https://liquidtelecom.dl.sourceforge.net/project/libpng/libpng12/older-releases/1.2.54/libpng-1.2.54.tar.xz
Хеш-сумма: cf85516482780f2bc2c5b5073902f12b1519019d47bf473326c2018bdff1d272
Дальше чини сам, ладно?
 Ri.
единственный бинарный установочный файл когорый на сайте циски был такой и скачал
а лучше поставь в виртуалку 18 убунту, поставь туда нативно трейсер версии 7.3 и развлекайся
Anonymous
Осталось пофиксить проблемы виртуалок, подмана, ostree. Дело за малым.
- https://github.com/containers/libpod/issues/6563
- https://github.com/containers/libpod/issues/6563
Виртуалки, подман, и флатпаки работают.
Но да, silverblue не хочет работать с btrfs. Проверял в виртуалке.
 Sergei
 Andreas
Подскажите как в nvidia settings добавить prime в Fedora 32?
Andreas
Quadro P3200 Mobile
Sergei
Quadro P3200 Mobile
Не уверен насчёт Quadro, но для новых чипов с драйвером 440.xx ничего не надо делать, prime offload работает из коробки.
Andreas
Не уверен насчёт Quadro, но для новых чипов с драйвером 440.xx ничего не надо делать, prime offload работает из коробки.
Спасибо. Просто на убунте можно было принудительно выбрать видеокарту через настройки
Sergei
Спасибо. Просто на убунте можно было принудительно выбрать видеокарту через настройки
Проприетарные драйверы стоят? Если да, покажи вывод xrandr --listproviders
Andreas
Проприетарные драйверы стоят? Если да, покажи вывод xrandr --listproviders
Providers: number : 2
Provider 0: id: 0x47 cap: 0xf, Source Output, Sink Output, Source Offload, Sink Offload crtcs: 3 outputs: 5 associated providers: 0 name:modesetting
Provider 1: id: 0x2ba cap: 0x0 crtcs: 0 outputs: 0 associated providers: 0 name:NVIDIA-G0
Sergei
Providers: number : 2
Provider 0: id: 0x47 cap: 0xf, Source Output, Sink Output, Source Offload, Sink Offload crtcs: 3 outputs: 5 associated providers: 0 name:modesetting
Provider 1: id: 0x2ba cap: 0x0 crtcs: 0 outputs: 0 associated providers: 0 name:NVIDIA-G0
Судя по всему, у тебя prime offload поддерживается и работает. Покажи ещё env __NV_PRIME_RENDER_OFFLOAD=1 __GLX_VENDOR_LIBRARY_NAME=nvidia glxinfo | head
Andreas
name of display: :0
display: :0 screen: 0
direct rendering: Yes
server glx vendor string: NVIDIA Corporation
server glx version string: 1.4
server glx extensions:
GLX_ARB_context_flush_control, GLX_ARB_create_context,
GLX_ARB_create_context_no_error, GLX_ARB_create_context_profile,
GLX_ARB_create_context_robustness, GLX_ARB_fbconfig_float,
GLX_ARB_multisample, GLX_EXT_buffer_age,
Sergei
name of display: :0
display: :0 screen: 0
direct rendering: Yes
server glx vendor string: NVIDIA Corporation
server glx version string: 1.4
server glx extensions:
GLX_ARB_context_flush_control, GLX_ARB_create_context,
GLX_ARB_create_context_no_error, GLX_ARB_create_context_profile,
GLX_ARB_create_context_robustness, GLX_ARB_fbconfig_float,
GLX_ARB_multisample, GLX_EXT_buffer_age,
Ну вот, используется дискретная видеокарта, ничего настраивать не трубется.
Andreas
по идее должна работать встроенная, т.к. никакой нагрузки нет
Andreas
а дискретную использовать только для отдельных приложений
Andreas
при запуске через меню
Sergei
по идее должна работать встроенная, т.к. никакой нагрузки нет
Дискретная и интегрированная с prime offload не переключаются эксклюзивно, а включаются по необходимости для отдельных приложений (типа как в винде).
__NV_PRIME_RENDER_OFFLOAD=1 __GLX_VENDOR_LIBRARY_NAME=nvidia делает ровно это - заставляет программу (glxinfo в данном случает) использовать дискретную видуокарту.
Andreas
Дискретная и интегрированная с prime offload не переключаются эксклюзивно, а включаются по необходимости для отдельных приложений (типа как в винде).
__NV_PRIME_RENDER_OFFLOAD=1 __GLX_VENDOR_LIBRARY_NAME=nvidia делает ровно это - заставляет программу (glxinfo в данном случает) использовать дискретную видуокарту.
в винде, если не ошибаюсь, вшит список приложений в драйвер для дискретной карты, а тут как определяется необходимость?
Sergei
в винде, если не ошибаюсь, вшит список приложений в драйвер для дискретной карты, а тут как определяется необходимость?
Тобой, вручную. Ещё предложили специальный параметр в .desktop-файле, указывающий, что программа предпочитает дискретную видеокарту, в Гноме вроде уже реализовано (или нет).
Andreas
Тобой, вручную. Ещё предложили специальный параметр в .desktop-файле, указывающий, что программа предпочитает дискретную видеокарту, в Гноме вроде уже реализовано (или нет).
в гноме отдельное контекстное меню есть для запуска на дискретном видео
Andreas
Еще есть вопрос. У меня Dell Developer Edition шел с убунтой. Dell обновил биос и после этого не просыпается ноутбук. Вот тут подробнее описано
https://www.reddit.com/r/Dell/comments/ebyo05/sleep_issues_on_dell_precision_7530/
Andreas
и там же решение
"Rolling back intel-microcode from 3.20191115.1ubuntu018.04.2 to 3.20180312.0~ubuntu18.04.1, and apt-mark hold intel-microcode seems to have fixed the problem for now."
Как откатить этот микрокод на федоре?
Sergei
и там же решение
"Rolling back intel-microcode from 3.20191115.1ubuntu018.04.2 to 3.20180312.0~ubuntu18.04.1, and apt-mark hold intel-microcode seems to have fixed the problem for now."
Как откатить этот микрокод на федоре?
Тебе не повезло, у нас как раз один чел, хорошо знакомый с ноутбуками, fwupd и вот этим всем, недавно свалил из Телеги.
Sergei
(
Если есть аккаунт в matrix, можешь зайти вот сюда https://matrix.to/#/!ORaJTQoYhvJzcPsgtM:matrix.org?via=matrix.org&via=russianfedora.online и спросить там @xvitaly:matrix.org
Andreas
аккаунта нет. Я так понимаю это интел на рукожопил?
Sergei
аккаунта нет. Я так понимаю это интел на рукожопил?
Я не в курсе. Вроде что-то мелькало про проблемное обновление микрокода.
ㅤ
🤔 https://github.com/hyakosm/simple_dnf
Sergey
Отличная находка же. Зарепортишь баг?
Сегодня ещё посмотрю
Если подтвердится, то зарепорчу в рхбз
Если нет, создам нового юзера и буду там смотреть
ㅤ
В RHBZ, да.
toobinks
Господа, подскажите как прочитать Rutoken S
toobinks
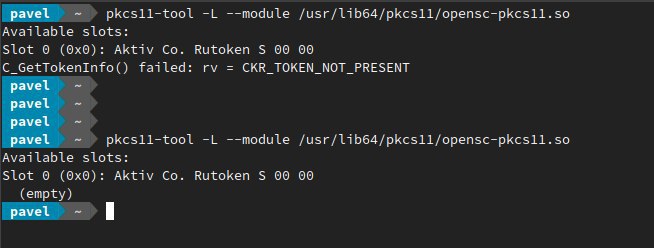
pkcs11-tool -L
Available slots:
Slot 0 (0x0): Aktiv Co. Rutoken S 00 00
C_GetTokenInfo() failed: rv = CKR_TOKEN_NOT_PRESENT
toobinks
делаю по этой статье https://www.altlinux.org/Rutoken#%D0%A0%D1%83%D1%82%D0%BE%D0%BA%D0%B5%D0%BD_S
Sergey
Anonymous
Почему?
Ты ведь про Silverblue спрашиваешь, да?
Если честно, то я уже не помню, почему система не грузилась, но точно помню - @Artem4 уже скидывал баг-репорт.
toobinks
для pkcs11-tool какая разница какой дистрибутив
Sergey
нет, fedora
И какого чуда ты ожидаешь?))
Эта поделка для работы требует libusb 0.1.7, который еще аж в шестом рхел поставлялся.
Тебе, очевидно, придется собрать/скачать эту библиотеку и подкладывать к ПО, которое они там поставляют
А еще лучше — прокинуть эту поделку в виртуалку и работать с ней там. Туда хоть винду ставь, хоть альт
toobinks
И какого чуда ты ожидаешь?))
Эта поделка для работы требует libusb 0.1.7, который еще аж в шестом рхел поставлялся.
Тебе, очевидно, придется собрать/скачать эту библиотеку и подкладывать к ПО, которое они там поставляют
А еще лучше — прокинуть эту поделку в виртуалку и работать с ней там. Туда хоть винду ставь, хоть альт
Каким образом из под свежей федоры вытащить с rutoken s ключ?
toobinks
Когда-то давно я это делал из под венды при помощи КриптоПро
ㅤ
Ты ведь про Silverblue спрашиваешь, да?
Если честно, то я уже не помню, почему система не грузилась, но точно помню - @Artem4 уже скидывал баг-репорт.
Их пачки. Для ostree в целом, не только Silver.
toobinks
И даже тогда давно из под федоры я мог использовать rutoken s из под федоры, кажется
Sergey
И даже тогда давно из под федоры я мог использовать rutoken s из под федоры, кажется
Ну, вряд ли. Допускаю, что это было 6-7 лет назад, но сейчас одной командой это сделать невозможно
toobinks
Т.е. из под федоры ключ с токена не вытащить?
Sergey
Там, если ты обратил внимания, рутокен с для работы требует собственный "драйвер", который в свою очередь требует очень старые версии библиотек, которых уже давно нет в федора
Sergey
Т.е. из под федоры ключ с токена не вытащить?
В теории это возможно, я же писал. Тебе нужно найти старый libusb, собрать "драйвер" рутокена используя хедер и саму libusb, установить его в систему (через make install, чего я однозначно не рекомендую) и надеяться на чудо
Sergey
Можно, конечно, в котейнер поставить что-нибудь старое и прокинуть туда усб
И уже в контейнере попытаться завести этот токен
Но с виртуалками будет проще))
toobinks
как-то всё заморочено
 Alexander
Там, если ты обратил внимания, рутокен с для работы требует собственный "драйвер", который в свою очередь требует очень старые версии библиотек, которых уже давно нет в федора
Там не нужен, по идее, драйвер. Должно работать через эмуляцию pkcs11 поверх pkcs15 средставми opensc.
toobinks
toobinks
драйвер для токена установлен - ifd-rutokens-1.0.4-1.x86_64
Alexander
драйвер для токена установлен - ifd-rutokens-1.0.4-1.x86_64
Зачем? Без него pkcs15-tool токен не видит?
toobinks
Зачем? Без него pkcs15-tool токен не видит?
Ну я кстати сейчас этот драйвер удалил и ошибка не появляется
toobinks
 Alexander
Ну я кстати сейчас этот драйвер удалил и ошибка не появляется
Просто сделай так, как сказано на вики альта. И не забудь указать модуль
toobinks
он теперь говорить , что токен пустой
Alexander
И что говорят pkcs15-tool с opensc?
toobinks
Я не говорил, что считаю, что ты бесплатно токен получил.
не, я имею в виду покупал токен с ЭЦП. т.е. он не пустой. я с него когда-то давно экспортировал ключ
Alexander
toobinks
в УЦ импортировали
toobinks
под вендой при помощи КриптоПро доставал pfx
Alexander
под вендой при помощи КриптоПро доставал pfx
Значит криптопрой же и экспортируй сейчас, если этот те же ключи. У тебя токен является pkcs15 хранилищем. Opensc хранит на нем данные, выставляя наружу pkcs11-интерфейс. То же самое делает и криптопро, но формат контейнеров на pkcs15 у cryptopro и opensc может не совпадать.
Alexander
Ты можешь попробовать глянуть, что за данные там лежат через pkcs15-tool или opensc
toobinks
Значит криптопрой же и экспортируй сейчас, если этот те же ключи. У тебя токен является pkcs15 хранилищем. Opensc хранит на нем данные, выставляя наружу pkcs11-интерфейс. То же самое делает и криптопро, но формат контейнеров на pkcs15 у cryptopro и opensc может не совпадать.
Да видимо только так и получится. Проблема только в том, что криптопро у меня сейчас больше нет
toobinks
Alexander
Там некое подобие фс
 Igor
Дата 2019, не знаю насколько всё это актуально на сегодняшний день. Но там не только это, много чего еще сильно медленнее:
https://www.phoronix.com/scan.php?page=article&item=linux-50-filesystems&num=2
tl;dr, I can make btrfs look awesome, and I can make it look stupid. It depends
on your workload, but generally speaking a normal Fedora user's workload is
going to feel the same regardless of the file system.
Phoronix is widely ignored and a joke to the fs development community. Facebook
deploys latency sensitive workloads across millions of machines with btrfs. We
do not accept latency regressions, our threshold for performance regressions
depends on the workload, but is generally under 5% and usually 1%.
That's not to say that btrfs is faster always, but that it depends on your
workload. The overwrite case is clearly a loser almost always, unless you use
the nocow file attr on those files. Reads can sometimes have higher latencies,
but that's the price you pay for checksumming. Inside Facebook we run with
compression on everywhere, which reduces the IO sizes both ways, which reduces
the overhead to the point where it's clearly faster than either xfs or ext4.
That's not the sole reason we use compression, but it's a nice way to get around
the cost of checksumming.
I'm currently knee deep in a performance discrepancy issue that WhatsApp has
discovered. However I have to get the file system to the point where it has > 1
TiB of metadata (not data, actual metadata) before I see a difference between
btrfs and xfs for that workload. Before that point it's not even a competition,
btrfs wins hands down. And even then we're talking about maximum latencies, so
every once and a while btrfs appears to go out to lunch for around 500ms for
unknown reasons.
These are the sort of performance investigations that btrfs is having right now,
edge cases under specific workloads. Generally speaking it's on par if not
faster than anybody else, and the cases where it's slower there's a clear trade
off being made for checksumming. Thanks,
Josef