 Sergey


Напомните статью или видео было, tricks для джумлы лайфхаки, там был пункт про изменение добавление пункта меню, в меню в админке
 Sergey
Напомните статью или видео было, tricks для джумлы лайфхаки, там был пункт про изменение добавление пункта меню, в меню в админке
В Joomla feed ищите hidden tricks
 Sergey
ну пздц =)
https://github.com/platformatic/php-node
теперь и нода может быть рантаймом для PHP =)
 Vladimir
ну пздц =)
https://github.com/platformatic/php-node
теперь и нода может быть рантаймом для PHP =)
Ну там вроде про общение между ними
Sergey
да
про то что PHP приложение можно заинджектить напрямую в nodejs приложение исходное
Sergey
пример есть в репе
позже разраб еще опишет наверно кейсы
но само по себе забавный тандем
Vladimir
пример есть в репе
позже разраб еще опишет наверно кейсы
но само по себе забавный тандем
Ну нода с php - частый кейс
Vladimir
Скажем так - хочешь пуши - это нода
Sergey
ну как отдельные составляющие
а не как embeded
 Eugene
https://x.com/tassosm/status/1927671314900218142
@progreccor крик души
 Павел
 Igor
https://x.com/tassosm/status/1927671314900218142
@progreccor крик души
А для тех кто прокси не доделал?
 RINAT
https://x.com/tassosm/status/1927671314900218142
@progreccor крик души
Ему надо сказать что надо использовать RadicalForm🙂
Dmitry
А для тех кто прокси не доделал?
Spam bots cracked the honeypot in our Joomla form builder extension.
We were proud of it. It had worked for years.
Then suddenly, a flood of betting links and garbage.
Time to rethink everything.
For years, we relied on a classic honeypot to stop spam:
• A fake input type="text"
• Hidden with CSS (display:none, positioned off-screen)
• Randomized field name/id like cf-field-xyz123
• Inserted server-side with PHP, part of the DOM
• Designed to trick bots into filling it out
It worked… until it didn’t.
Bots evolved.
They ignore display:none, detect name patterns, scan for “trap” fields.
Eventually, spam shot up. It was time to fight back.
I was convinced bots could now run JavaScript.
So I rebuilt the honeypot from scratch — this time, fully JS-based.
• It is injected via JavaScript after the form is ready
• It uses a random, unique name/id per session
• It’s hidden with inline CSS (display:none) targeting its unique ID.
• The field is added to the payload
On the server side, the logic is simple:
If the honeypot field is missing or not empty, it’s flagged as spam.
Now here’s the interesting part:
I expected bots to fill the honeypot. Instead, every flagged submission had the field missing entirely from POST data.
🤯 That means bots couldn’t run the JS that generates the field.
Is this a headless browser limitation? A shortcut to skip JS after page load?
No idea. But it works.
Spam dropped.
No CAPTCHAs. No friction.
Just one invisible field they keep missing.
If you’ve got theories, I’m all ears.
Igor
• A fake input type="text"
• Hidden with CSS (display:none, positioned off-screen)
• Randomized field name/id like cf-field-xyz123
• Inserted server-side with PHP, part of the DOM
• Designed to trick bots into filling it out
это же ни от кого не помогает =)
Dmitry
Ну пишет, что помогло в итоге
Dmitry
Js решение
Igor
Все что он описал можно заменить на токен который получаеться ajax пред оправкой =)
Dmitry
Просвети неуча 🙂
Igor
Эм?
csrf заменит все что он сделал. У него боты это простоые парсим стрницу видим форму отправляем.
Igor
постом.
Dmitry
csrf заменит все что он сделал. У него боты это простоые парсим стрницу видим форму отправляем.
А может у него нет form, он просто это называет формой
Dmitry
Я туплю
Dmitry
Как помогает csrf
Dmitry
Csrf не генерится для ботов?
Dmitry
Блин, реально туплю 🙂
Dmitry
Ааа
Igor
Csrf не генерится для ботов?
На ajax у многих ботов нет. Тебе нужен бот способный выполнять js читающий ajax и обновляющий сессиию на лету.
Vladimir
Ну скажем так - помогает все равно от тупых
Vladimir
Полноценный браузер сожрет
Igor
Но и то что он сделал тоже самое.
Vladimir
Борьба с ботами ведутся на уровне поведенческих и контентных
Vladimir
А так же контролем ip
Igor
Борьба с ботами ведутся на уровне поведенческих и контентных
Война с ботами в форме ведется путем сообщений "@progreccor там боты в радикалформ пробились"
Igor
А RM ведеться путем. Только самый отбитый бот будет полностью оформлять заказ =)
Vladimir
А RM ведеться путем. Только самый отбитый бот будет полностью оформлять заказ =)
Если у бота есть деньги то мы продадим и боту
Eugene
Ему надо сказать что надо использовать RadicalForm🙂
не надо. пусть у форм останется конкурентное преимущество
Sergey
 Sergey
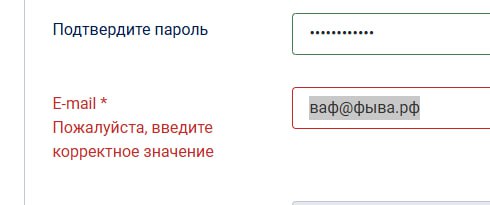
Емейлы на кириллице у юзеров - кто как побеждал?
Sergey
 Александр
Емейлы на кириллице у юзеров - кто как побеждал?
до собаки должна быть латиница, на сколько я знаю
Vladislav
Вы же знаете вот об этом:
На российских сайтах сейчас разрешена регистрация только с email-адресов, принадлежащих доменам, зарегистрированным в российских дата-центрах и внесённым в реестр отечественных почтовых сервисов Роскомнадзора.
 Alexey
Коллеги, а нет такого сервиса - ввел домен, проверил и получил - ваш сайт соответствует требованиям
Alexey
Vladislav
А как быть с англоязычной версией ?
Если европеец заходит на сайт, то начинает дейстовать GDPR уже, там свои правила. Плюс в некоторых странах накладываются локальные законы
Vladimir
Емейлы на кириллице у юзеров - кто как побеждал?
Вообще это некорректный формат. По сути не существует кириллических почтовых адресов
Vladimir
Они не проходят проверку
Александр
Они не проходят проверку
если до @ будет латиница info@домен.рф то проверку такая почта пройдет
Vladimir
если до @ будет латиница info@домен.рф то проверку такая почта пройдет
Формально домена кириллического не существует - используется кодировка puny code
Vladimir
Да и вообще кириллические домены в почте практически не работают - почта толком не ходит
Vladimir
В отличие от браузеров протоколы обмена емейл не поддерживают кириллицу. Так что кириллические домены работают только в Яндекс почте и то с трудом
Igor
/**
* Method to process Core Content Plugins Events.
*
* @param object $item Modification item.
*
* @since __DEPLOY_VERSION__
*/
protected function processContentPlugins(object $item): void
{
$dispatcher = $this->getDispatcher();
PluginHelper::importPlugin('content', null, true, $dispatcher);
$arguments = [
'context' => $this->context,
'subject' => $item,
'params' => $item->params,
'page' => (int) $this->state->get('list.offset'),
];
$dispatcher->dispatch('onContentPrepare', new ContentEvents\ContentPrepareEvent('onContentPrepare', $arguments));
// Extra content from events
$item->event = new \stdClass();
$contentEvents = [
'afterDisplayTitle' => new ContentEvents\AfterTitleEvent('onContentAfterTitle', $arguments),
'beforeDisplayContent' => new ContentEvents\BeforeDisplayEvent('onContentBeforeDisplay', $arguments),
'afterDisplayContent' => new ContentEvents\AfterDisplayEvent('onContentAfterDisplay', $arguments),
];
foreach ($contentEvents as $resultKey => $event)
{
$results = $dispatcher->dispatch($event->getName(), $event)->getArgument('result', []);
$item->event->{$resultKey} = $results ? trim(implode("\n", $results)) : '';
}
}
Кто у нас там компоненты перебирает. Полезное для view
Sergey
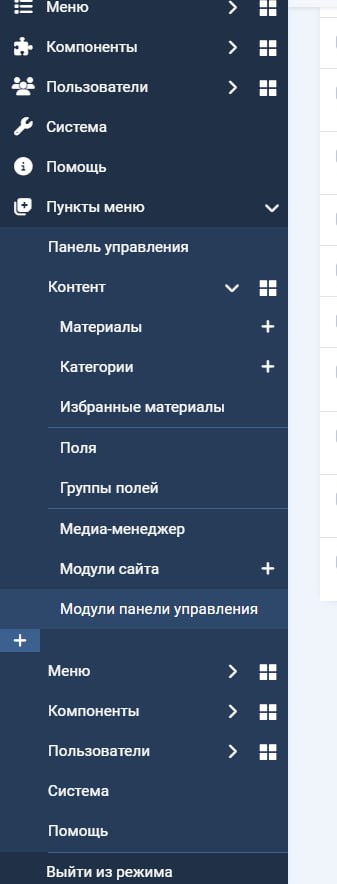
привет при добавлении модуля меню в административно части выдает такое предупреждение Меню панели управления Меню администратора не содержит пункты Меню, Модули, Контейнер компонентов. Войдите в режим восстановления меню. вхожу в режим что дальше делать?
 Sergey
 Виталий
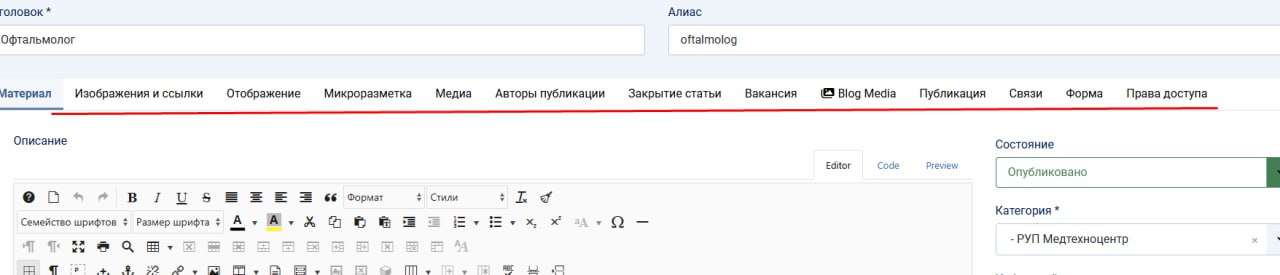
А что именно изменить?
Виталий
Скрыть по разному можно
 Дмитрий
 Eugene
https://www.itoctopus.com/a-quick-guide-to-optimizing-joomla-5-by-disabling-plugins
интересное исследование. @vitalik_a можешь перевести, если будет желание
Vladimir
Vladimir
там только емейл бесполезный
 Дмитрий
там только емейл бесполезный
ага, это бек, а посмотрим на фронт, картинки по 16мб, на sp builder сделано, где там каша из стилей и много всего тянется
Дмитрий
и толку в целом никакго, тут комлпекс
Дмитрий
сервера теже, диски, файловая система и много чего еще
Vladimir
там даже много зависит как сам сайт организован
Дмитрий
https://www.itoctopus.com/a-quick-guide-to-optimizing-joomla-5-by-disabling-plugins
интересное исследование. @vitalik_a можешь перевести, если будет желание
а посыл в целом, отключите тем что не используете
Дмитрий
пройтись по расширениям и отключить
Дмитрий
что собственно я и делаю тоже
Eugene
а если включено стандартное кэширование, то это уже не играет роли?