 Dima

 Dima
а где потом посмотреть эти логи?
Dima
https://www.prajwaldesai.com/sccm-client-log-collection/
 System Center Bot
Configuration Manager news:
Quickly Turn Off AutoPlay Using Intune https://www.anoopcnair.com/turn-off-autoplay-using-intune-mem/
Anton
Господа, я правильно понимаю что при наличии гпо с указанием всус сервера, клиенты сццм не будут ставить апдейты которые развёрнуты через него? При условии что в гпо указан отличный от сайта сццм всус.
 Sergey
последнее предложение не понимаю
Sergey
отличный от сайта сццм всус
Sergey
если вы политикой укажете сервер всус клиент будет ходить к тому серверу всус (остальные параметры тоже нужны)в независимости отдельно стоящий это всус или в инфраструктуре CM
Anton
отличный от сайта сццм всус
Отличающийся. У меня есть 2 всуса которые распространяют апдейты винды.
На ццм свой всус естественно свой через него апдейты офиса 365.
Anton
И я именно в контексте обновлений office 365.
Sergey
ну вот клиент (метадата+контент) паблишится только на свой всус (когда выбираешь что хочешь ставить клиента таким образом в сайте)
Sergey
там отдельный вендор
типа Locаl published, или как то так называется
Anton
ну вот клиент (метадата+контент) паблишится только на свой всус (когда выбираешь что хочешь ставить клиента таким образом в сайте)
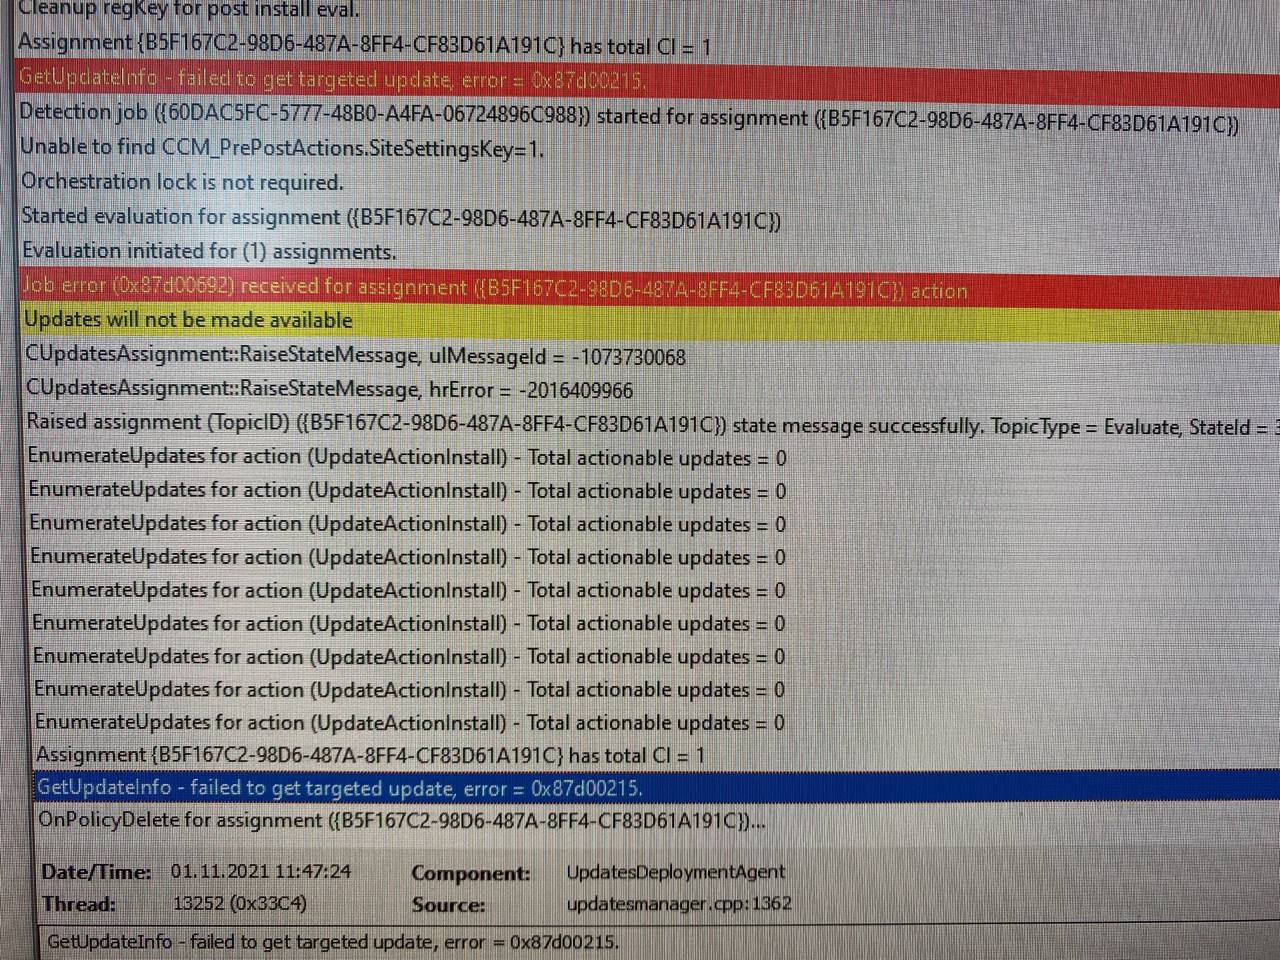
Ну клиент у меня ставится обычным аппом. И вот ловлю в логе updatesdeployment:
Anton
 Sergey
gp конфликт
Sergey
кажется что схема с двумя разными, одновременно живущими всус-ами, смотрится не очень
Anton
кажется что схема с двумя разными, одновременно живущими всус-ами, смотрится не очень
Понял, плохо тогда. Начальство пока не готово к апдейтам винды через ссм. Хотел в пилоте им пока апдейты офиса показать.
Sergey
на группами там выкусить часть машин
и политикой только на этим машины SUP
 Vladislav
А разве ссм клиент не перебивает настройки гпо? Он же пропишет правильные сервер, а логе будет сказано, мол, через гпо прилетают другие настройки, но машина будет юзать настройки клиента
 Vasya
нет
Vasya
агент ццм юзает локал гпо
Vasya
lsdou
Quantum Yupiter
Я ж писал как делать. Сделать ад группу, в сццме из неё сделать коллекцию для пилота и натравить клиентскую настройку.
Потом в GPO поставить Deny для группы
Dmitry
Коллеги, всем привет!
В TP 1906 и 2009 анонсировался Remote Control over CMG.
Кто-нибудь в курсе, в итоге эту фичу включили в последние релизы или нет?
 Rishat
Quantum Yupiter
Коллеги, всем привет!
В TP 1906 и 2009 анонсировался Remote Control over CMG.
Кто-нибудь в курсе, в итоге эту фичу включили в последние релизы или нет?
Не стоит рассчитывать на её включение в релиз
Quantum Yupiter
Почему?
Потому что код написан еще в 2019 году, а до релиза до сих пор дело не дошло
Anton
А разве ссм клиент не перебивает настройки гпо? Он же пропишет правильные сервер, а логе будет сказано, мол, через гпо прилетают другие настройки, но машина будет юзать настройки клиента
Пытается) но в итоге по логам видно что не может.
Anton
Я ж писал как делать. Сделать ад группу, в сццме из неё сделать коллекцию для пилота и натравить клиентскую настройку.
Потом в GPO поставить Deny для группы
Не все так просто. Даже после денай на все политики которые пушат политики всус - идёт эта ошибка.
Удаление руками registry.pol и перезапуск sms host.
Печаль если на всех тачках придётся делать.
Sergey
А если включить peer cache в политике, но отключить в свойствах boundary group параметр Allow peer downloads in this boundary group. то peer cache будет работать, пока клиент не поймет что он в другой boundary group?
Vasya
Quantum Yupiter
К тому же можно, думаю, через Scripts гордо накатить везде
Vasya
Не все так просто. Даже после денай на все политики которые пушат политики всус - идёт эта ошибка.
Удаление руками registry.pol и перезапуск sms host.
Печаль если на всех тачках придётся делать.
@panin выгрузи, я что-то не помню откуда его накопал. там чувак прям расследование провел
Dmitry
такие полезные вещи надо хранить в закладках)
Vasya
ну я же знаю, где его можно взять
Sergey
https://t.me/configmgr/115620
Dmitry
<#
.SYNOPSIS
Check for local Policy corruption issue
.DESCRIPTION
Checks the local policy files for corruption Then remediates if found
.ACKs TO this blog - we just added the user part..
https://itinlegal.wordpress.com/2017/09/09/psa-locating-badcorrupt-registry-pol-files/
.NOTES
AUTHOR: 2Pint Software
EMAIL: support@2pintsoftware.com
VERSION: 1.0.0.0
DATE:07/03/2018
CHANGE LOG:
1.0.0.0 : 07/03/2018 : Initial version of script
.LINK
https://2pintsoftware.com
#>
#Main Function which checks the policy files for corruption
Function Test-IsRegistryPOLGood
{
$PathToMachineRegistryPOLFile = "$ENV:Windir\System32\GroupPolicy\Machine\Registry.pol"
$PathToUserRegistryPOLFile = "$ENV:Windir\System32\GroupPolicy\User\Registry.pol"
# Test for a Machine policy file - if there isn't one - all good
if(!(Test-Path -Path $PathToMachineRegistryPOLFile -PathType Leaf)) {}
#If there is a .pol file - test it
else{
If (((Get-Content -Encoding Byte -Path $PathToMachineRegistryPOLFile -TotalCount 4) -join '') -ne '8082101103'){Return $False}
}
# Test for a User policy file - if there isn't one - as you were
if(!(Test-Path -Path $PathToUserRegistryPOLFile -PathType Leaf)) {}
#If there is a .pol file - test it
else {
If (((Get-Content -Encoding Byte -Path $PathToUserRegistryPOLFile -TotalCount 4) -join '') -ne '8082101103'){Return $False}
}
#if we made it here alles gut
return $true
}
#Set the default
$Compliance = "Compliant"
#Then test the policy file using the function above - returns non-compliant if EITHER machine/user policy file is found to be corrupt.
If ((Test-IsRegistryPOLGood) -eq $true)
{
$Compliance = "Compliant"
}
else
{
$Compliance = "Non-Compliant"
}
$Compliance
Dmitry
https://itinlegal.wordpress.com/2017/09/09/psa-locating-badcorrupt-registry-pol-files/
Dmitry
https://itinlegal.wordpress.com/2017/09/09/psa-locating-badcorrupt-registry-pol-files/
@snowdeath в закладки добавь)
Dmitry
icloud/google
Vasya
в телеге храню обычно
Vasya
и в onenote
Dmitry
и в onenote
сначала хранишь локальную базу onenote, а потом они делают, что можно только из вандрайва
Dmitry
спасибо не надо
Vasya
ну 2016 жив еще
Anton
icloud/google
Кстати, для замёток на яблоке что посоветуешь?
Стандартные так себе после ванноута.
Dmitry
Кстати, для замёток на яблоке что посоветуешь?
Стандартные так себе после ванноута.
я просто перестал хранить заметки))
Dmitry
только сайты в закладках
Dmitry
пароли keepassXC
Dmitry
а на телефоне только в гугл хроме вкладки храню))
Dmitry
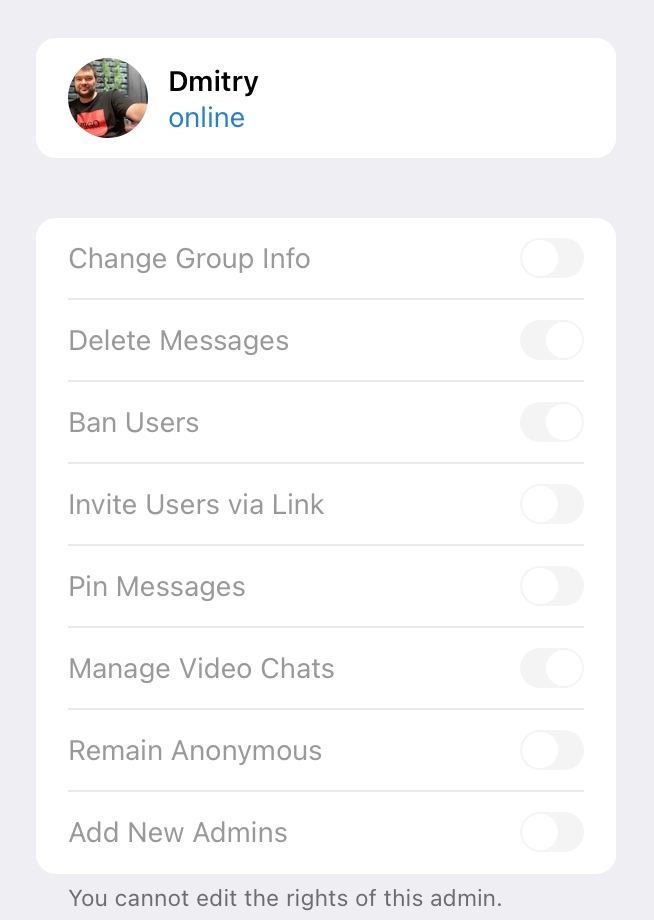
@masyan надо снова @skorotkov короновать)
он почему-то не админ
Sergey
не надо, я устал :)
Dmitry
устал пинить вакансии?)))
Sergey
да
Dmitry
тогда нужны права без пинилки)
Dmitry
как у меня
Sergey
не нужны :)
я не понял что можно пинить и не можно, поэтому
Dmitry
 Sergey
@Panin Дима а кто будет собес проводить на открывшуюся вакансию?
Vasya
+рук
Alexander